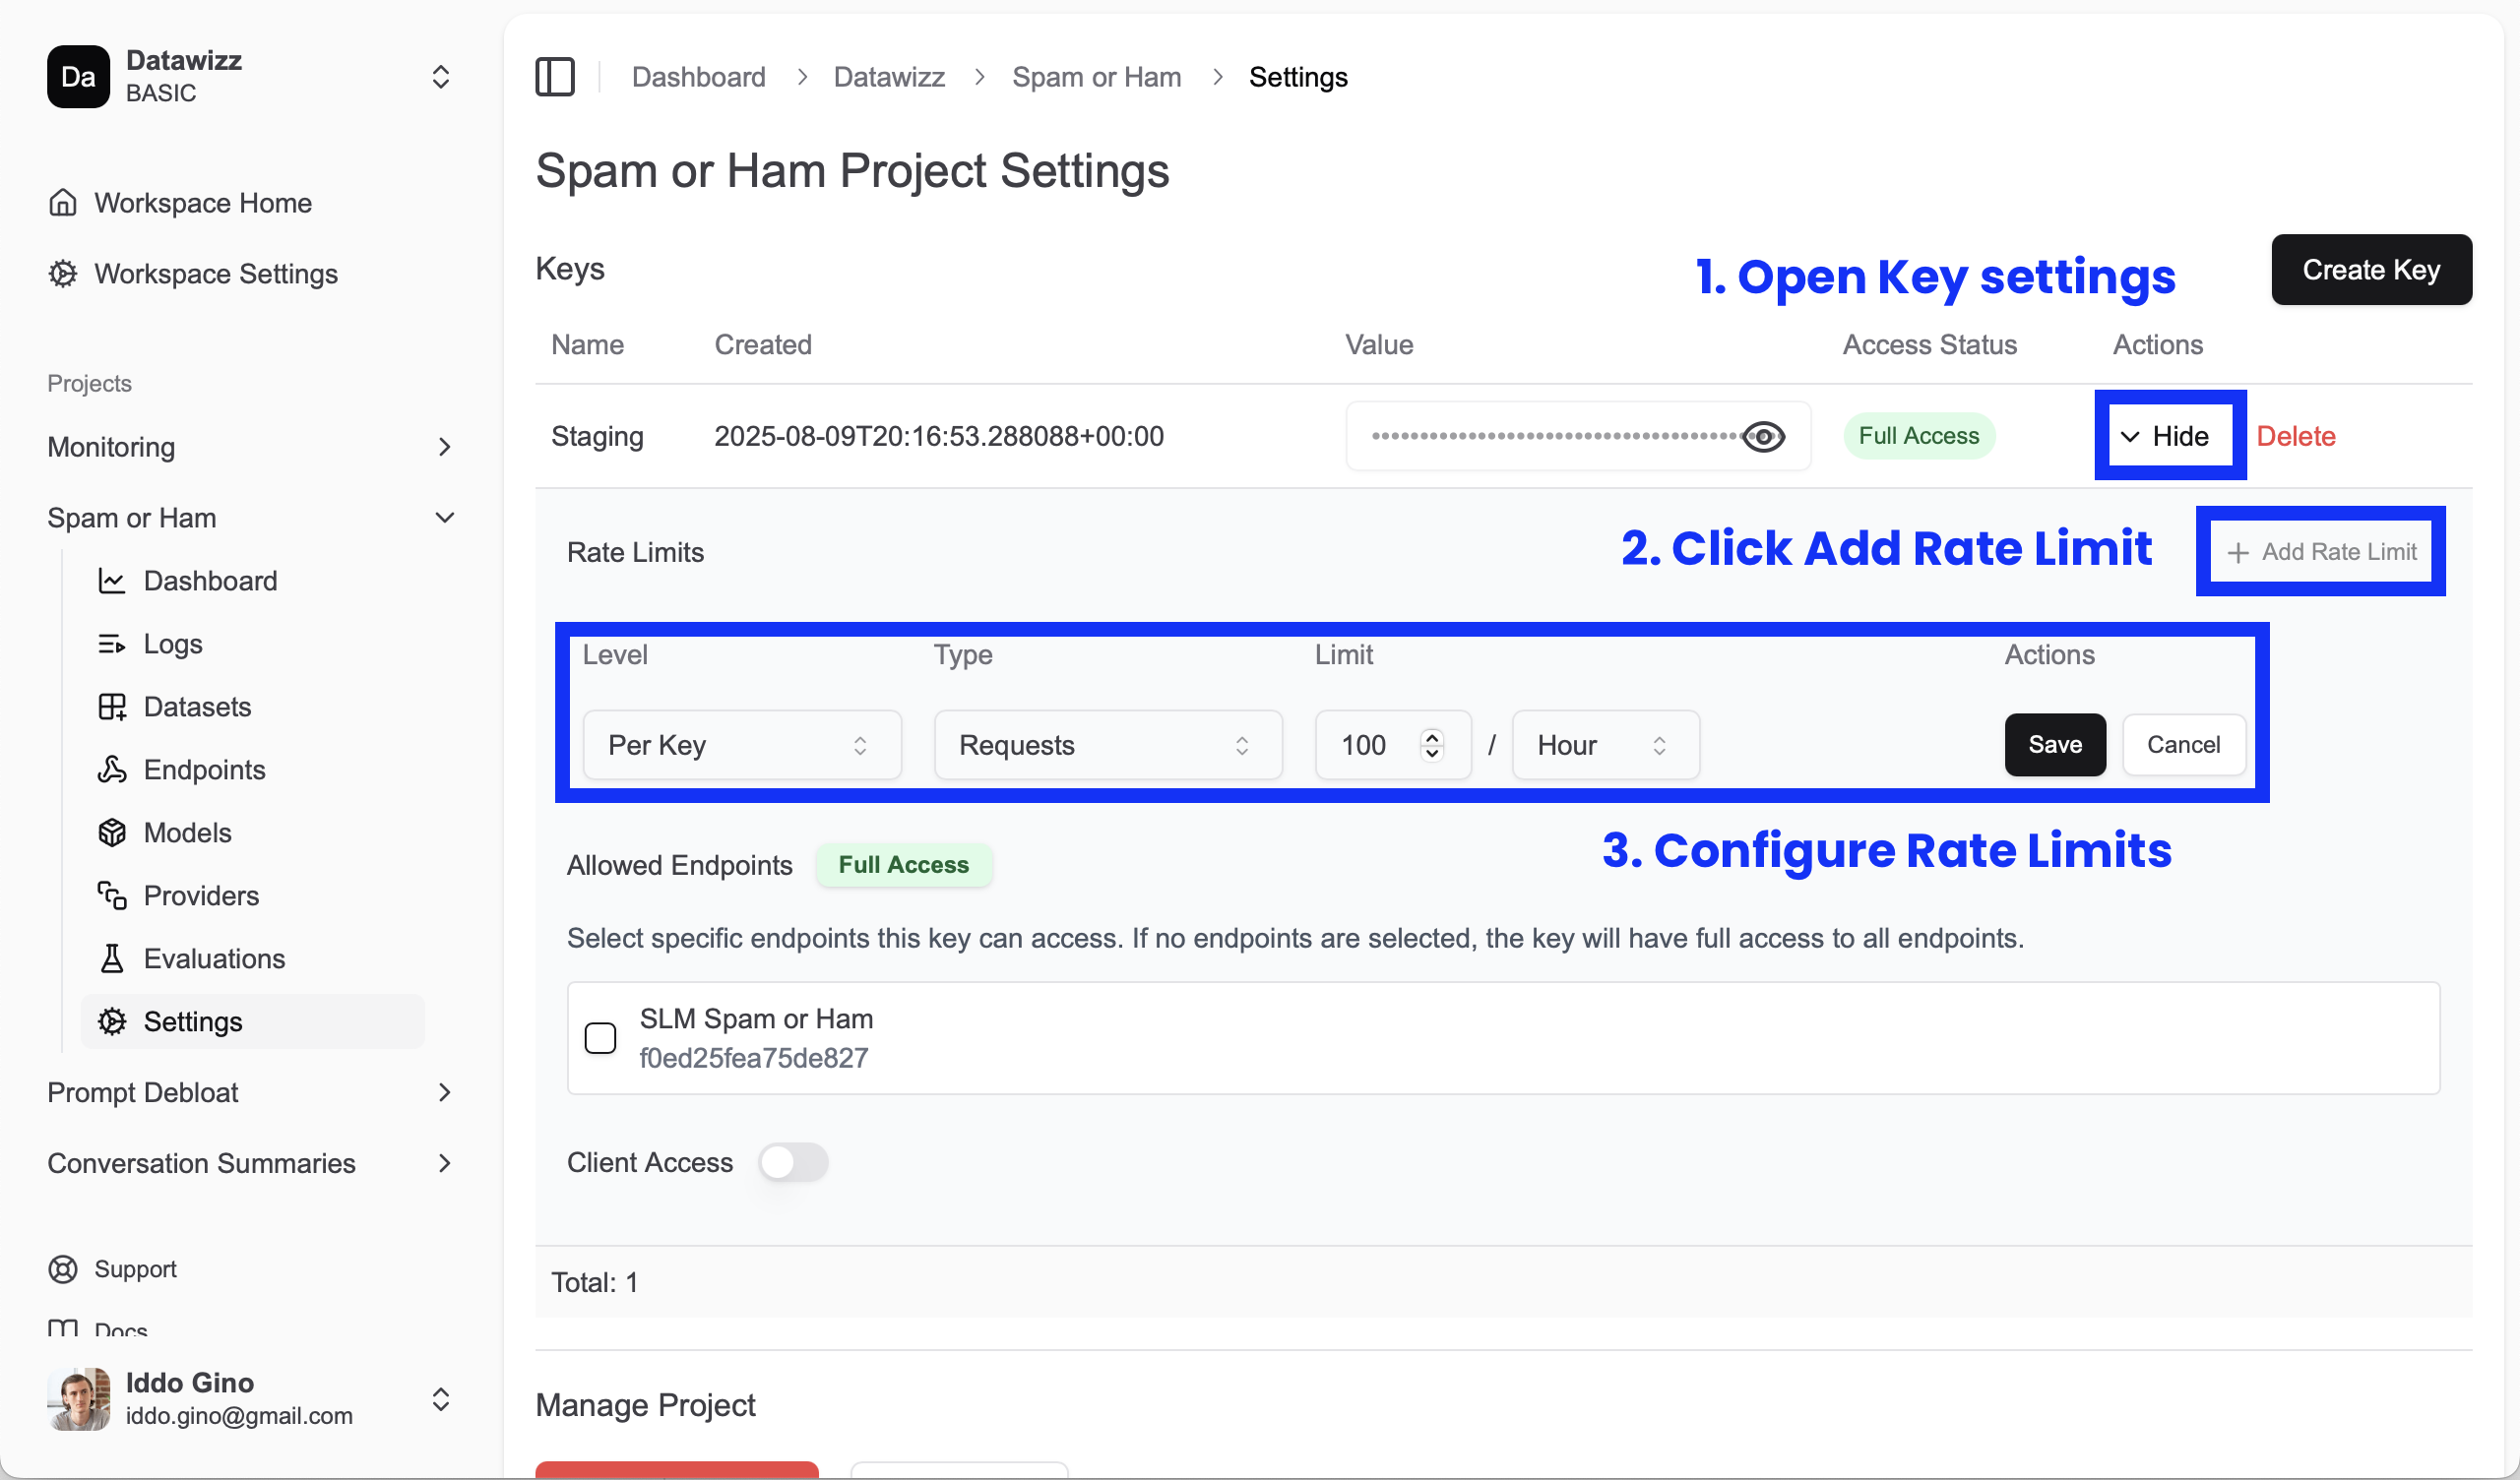
Rate limits provide fine-grained control over API usage, allowing you to prevent abuse and manage resource consumption effectively. The system supports both key-level and user-level limits with multiple resolution types.
Rate limits are managed at the Project Key level - so you can set different limits for different keys (e.g. production key can have different limits than development key).To add a rate limit to a key:
Go to the Settings page of your project.
Select the key you want to configure.
Click on Add Rate Limit.
Configure the limit type, resolution, and value.
Save the changes.
The limit will be applied immediately and enforced on all requests using that key.
The system collects usage metrics even before you configure rate limits. So when adding a rate limit, it’ll take into account all historical usage data.
Usage tracking is aligned to clock and calendar time — so an hourly limit resets every hour, a daily limit resets at midnight (UTC), and a monthly limit resets at the start of each month. The system supports the following resolutions:
All configured rate limits are checked simultaneously. If ANY limit is exceeded, the request is blocked.Example scenario:
Configured limits:- Key-level: 1,000 requests per hour- User-level: 100 requests per hourIf user has made 99 requests this hour:- User limit: 99/100 ✅ (allowed)- Key limit: 850/1,000 ✅ (allowed)- Result: Request allowedIf user has made 100 requests this hour:- User limit: 100/100 ❌ (exceeded)- Key limit: 851/1,000 ✅ (allowed)- Result: Request blocked (429 status)